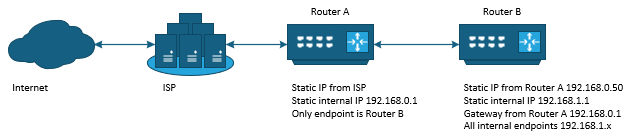
In order to set up Let’s Ecrypt on a Raspberry Pi 4 running Home Assistant, I am tring to set up port forwarding, because port 80 on the Raspberry Pi 4 (Home Assistant) must be reachable from outside when Let’s Encrypt creates a certificate.
In Let’s Ecrypt’s log, I read:
Certbot failed to authenticate some domains (authenticator: standalone). The Certificate Authority reported these problems:
  Domain: (mydoimain).duckdns.org
  Type:   connection
  Detail: (ip.ip.ip.ip): Fetching http://(mydomain).duckdns.org/.well-known/acme-challenge/something: Timeout during connect (likely firewall problem)
Hint: The Certificate Authority failed to download the challenge files from the temporary standalone webserver started by Certbot on port 80. Ensure that the listed domains point to this machine and that it can accept inbound connections from the internet.
I have verified my Raspberry Pi 4’s port 80 to be open for some seconds after Let’s Encrypt has this in its log:
Requesting a certificate for (mydomiain).duckdns.org
Namely, I get this:
$ nc -vz 192.168.1.194 80
homeassistant.fritz.box [192.168.1.194] 80 (http) open
I assume the problem is with my router. I have read that other services listening on port 80 might be a problem, but when I nmap my router using nmap to its outside URL, and with the port forwarding table empty, I get:
~$ nmap -Pn -p80,443,8123 (mydomain).duckdns.org
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-04 17:38 CEST
Nmap scan report for (mydomain).duckdns.org (ip.ip.ip.ip)
Host is up.
rDNS record for ip.ip.ip.ip: aftr-ip-ip-ip-ip.dynamic.(myprovider).de

PORT     STATE    SERVICE
80/tcp   filtered http
443/tcp  filtered https
Once I create a forwarded port in the router’s settings, namely port 80 (external) to port 80 of my Raspberry Pi 4 (HomeAssistant) for TCP, this is still the same. Even just after :
Requesting a certificate for `(mydomiain).duckdns.org`:
Shows up in the log, nmap has still the same output as above. However, nc shows a fwd/rev mismatch:
$ nc -vz (mydomain).duckdns.org 80
DNS fwd/rev mismatch: (mydomain).duckdns.org != aftr-ip-ip-ip-ip.dynamic.(myprovider).de
This leads me to believe that my ISP does something I need to consider when setting up DuckDNS (IPv4 / IPv6) or it is maybe a mistake to set up both IPv4 and IPV6 in the router’s port forwarding rules?
Update: Here’s one more thing that I don’t understand: My router lists only a few ports for provider’s services as open to the internet, namely:
5060
7078-7097
8089
However, when I nmap my ipv6 address, I get:
$ nmap -Pn -6 -p80,443 (ipv6:ipv6:ipv6:ipv6:ipv6:ipv6:ipv6:ipv6)
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-04 18:06 CEST
Nmap scan report for (ipv6:ipv6:ipv6:ipv6:ipv6:ipv6:ipv6:ipv6)
Host is up (0.00067s latency).

PORT     STATE  SERVICE
80/tcp   open   http
443/tcp  open   https
Why do ports 80 and 443 for http and https seem to be open even though my router does not list them as open? Is my ISP catching them, and are they thus unusable for me when I try to set up Let’s Encrypt via http, and do I need to choose dns instead in Let’s Encrypt’s settings?